NIST Cloud Security Best Practices for SaaS Startups
Flexible federal guidance on identity, access, and data isolation for resource-constrained teams.
Nadia Serrano
Flexible federal guidance on identity, access, and data isolation for resource-constrained teams.
Pick your compliance path based on where your buyers are, not which framework sounds better.
Auditors demand documented proof of least privilege, not just policy intentions and good intentions.
Small teams can achieve SOC 2 compliance by narrowing scope strategically.
Customer misconfiguration, not platform flaws, drives most Azure healthcare data breaches.
Learn which managed Postgres provider fits your workload and how to migrate cleanly.
Shared infrastructure exposes every tenant to the same vulnerabilities simultaneously.
Four architectural choices determine whether a self-hosted PaaS truly supports multi-cloud.
How to separate real bring-your-own-cloud from vendor marketing.
Reorder Dockerfile layers and cache package managers to cut CI build times by 70-90 percent.
Backward compatibility and staged migrations make schema changes safe for automated deployment.
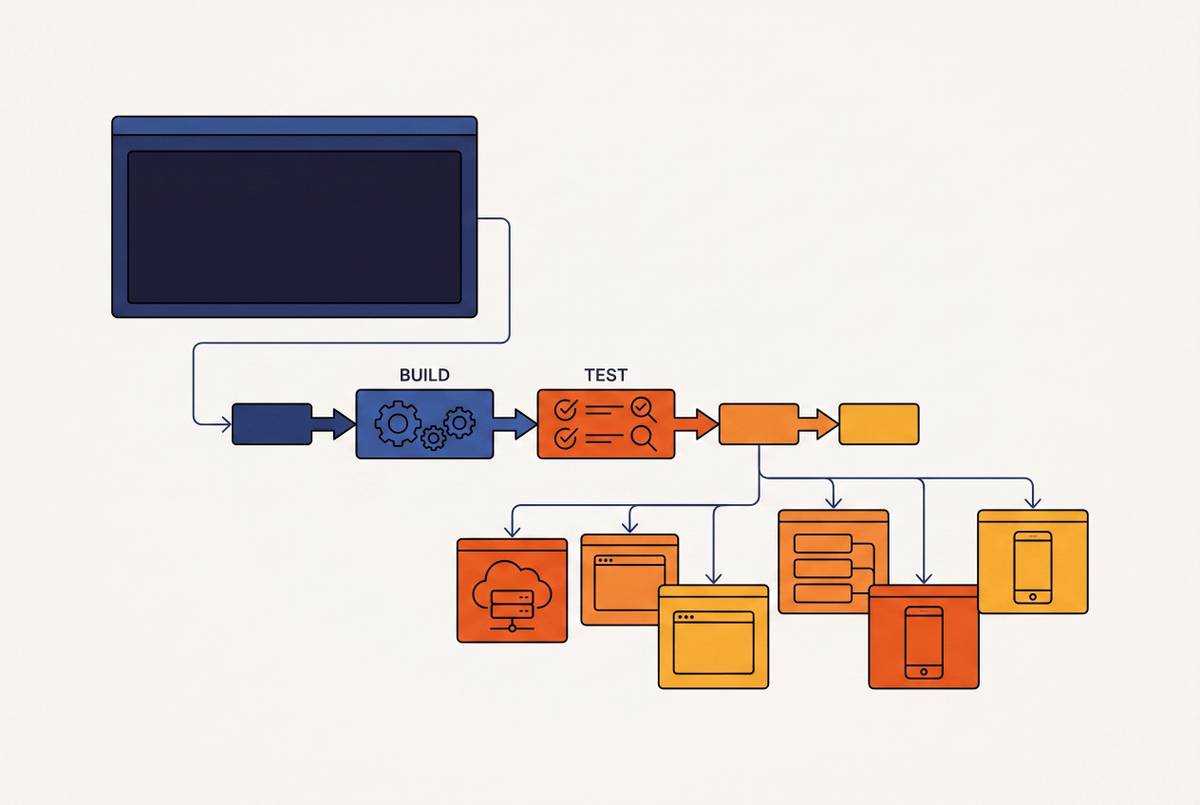
Architectural decisions about change detection and deployment scope matter more than tool choice.