 Internal Developer Platforms & Self-Hosted Tooling
How Compliance-Bound Engineering Teams Lock an AI App Builder Inside Their Own Cloud Perimeter
Keep the builder out of production, and PHI stays inside your VPC.
Owen Nystrom·
 Internal Developer Platforms & Self-Hosted Tooling
Deploying a Private AI App Generator in a Fully Air-Gapped Cloud Account for Internal Business Applications
How to build an AI system that stays completely disconnected from the internet.
Owen Nystrom·
 PaaS Alternatives
Who Actually Owns the AWS Resources When Your PaaS Deploys to Production
BYOC puts production resources in your account, while shared-tenant PaaS keeps them in the vendor's.
Owen Nystrom·
 Cloud Compliance
Terraform Modules That Ship HIPAA and SOC 2 Controls as Default AWS Infrastructure Primitives
Enforce compliance controls before deployment, not during audits.
Owen Nystrom·
 Internal Developer Platforms & Self-Hosted Tooling
Self-Hosted AI App Builders for Internal Tools
Control and compliance shape which self-hosted AI builder fits your team's constraints.
Owen Nystrom·
 Internal Developer Platforms & Self-Hosted Tooling
Internal Tooling Platforms Compared for Engineering Teams Without a Frontend Dev
Choose the IDP that solves your bottleneck, not the fanciest interface.
Owen Nystrom·
 Cloud Compliance
Compliance as Infrastructure Code When You Have No One to Own It
Platform-enforced compliance controls eliminate the owner gap for early-stage startups.
Owen Nystrom·
 PaaS Alternatives
Tenant Isolation Models in Modern PaaS and What They Mean for Your Cloud Bill
How you split tenants across infrastructure shapes your cloud costs more than any code optimization.
Owen Nystrom·
 Features
How NIST CSF Maps to Real AWS and GCP Controls
NIST's framework translates into cloud controls through AWS and GCP services.
Owen Nystrom·
 Features
AWS Infrastructure Controls That Satisfy HIPAA Requirements
Healthcare organizations must configure AWS controls themselves to achieve HIPAA compliance.
Owen Nystrom·
 Features
Jenkins vs GitHub Actions for Small Engineering Teams
Infrastructure overhead, not syntax, determines which tool fits a lean engineering team.
Owen Nystrom·
 PaaS Alternatives
open-source self-hosted PaaS options for multi-cloud deployments
Four architectural choices determine whether a self-hosted PaaS truly supports multi-cloud.
Owen Nystrom·
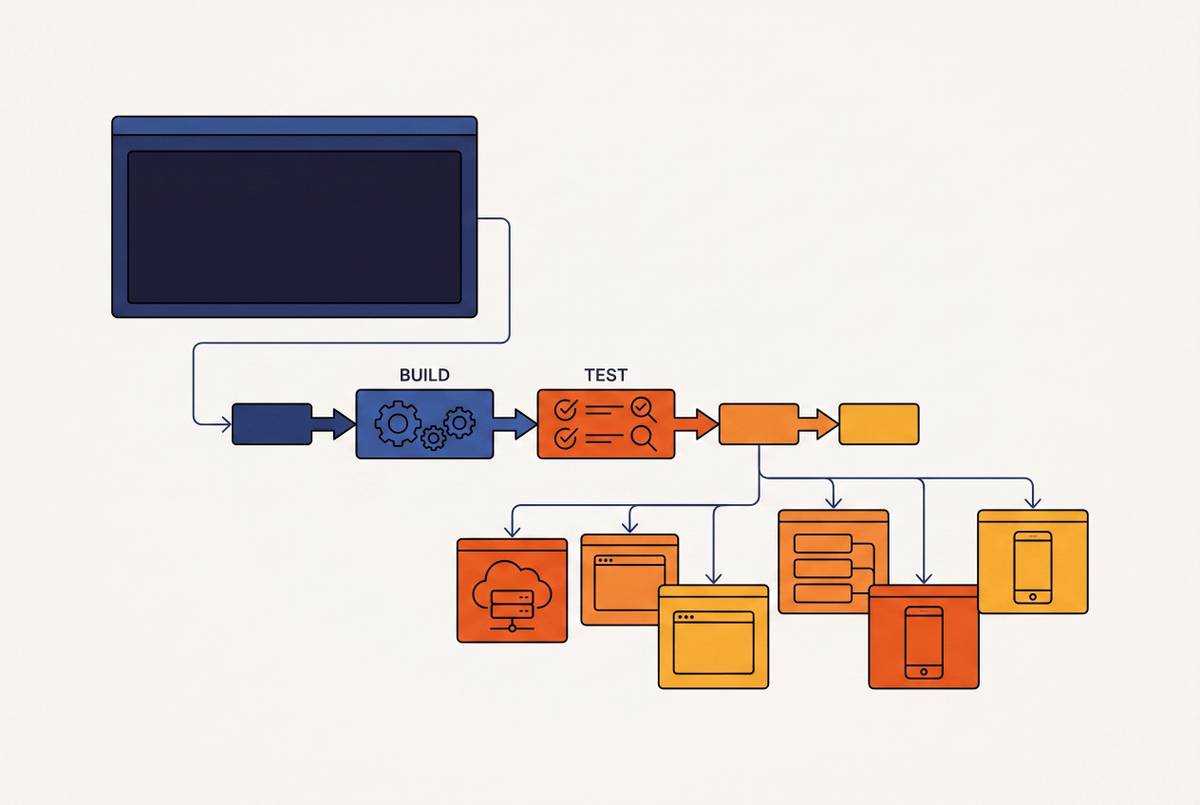 CI/CD Workflows
Monorepo CI/CD Architecture for Multi-Service Startups
Architectural decisions about change detection and deployment scope matter more than tool choice.
Owen Nystrom·
 DevOps Automation
Automating Kubernetes Cluster Upgrades Without Downtime
Automated pre-flight checks and rolling upgrades keep Kubernetes current without downtime.
Owen Nystrom·
 Cloud Compliance
SOC 2 Type II Compliance on AWS for Startups
How startups can achieve the security audit enterprise buyers now require to close deals.
Owen Nystrom·
 PaaS Alternatives
Fly.io vs AWS for Startup Production Workloads
Engineering time or compute cost: which resource matters more at your startup's stage.
Owen Nystrom·
 CI/CD Workflows
Managing Secrets Injection Across Multiple Deployment Environments
Unscoped credentials across environments turn leaked secrets into organization-wide breaches.
Owen Nystrom·
 CI/CD Workflows
Blue-Green vs Canary Deployment Strategies for Production Services
Blue-green rolls back instantly; canary limits blast radius.
Owen Nystrom·
 CI/CD Workflows
Preview Environments for Pull Requests on Kubernetes
Each pull request gets its own isolated environment.
Owen Nystrom·
 CI/CD Workflows
GitHub Actions CI/CD Pipeline for Kubernetes Deployments
Split your CI/CD pipeline into three files to separate concerns and secure production credentials.
Owen Nystrom·
 Compliance & Security
Container Image Security Scanning in CI/CD Pipelines
Effective scanning requires coverage at build, registry.
Owen Nystrom·
 CI/CD Workflows
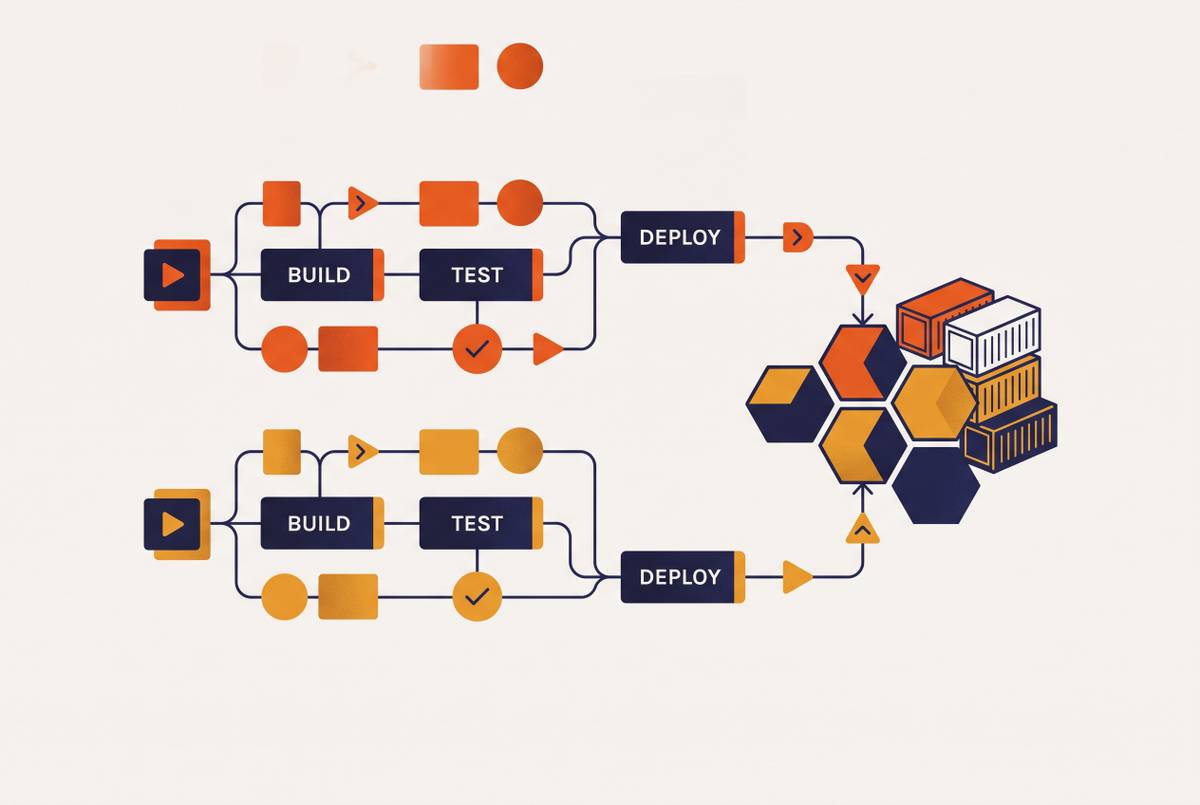
GitHub Actions vs GitLab CI for Kubernetes Deployments
GitHub Actions scales modularly; GitLab CI owns the entire DevOps stack.
Owen Nystrom·